The exchange has pledged to cover the losses as investigators trace stolen assets, examine suspected North Korean involvement and work towards restoring withdrawals.
Global | Business News, Cryptocurrency and Cybersecurity
Information checked on 31 October 2026.
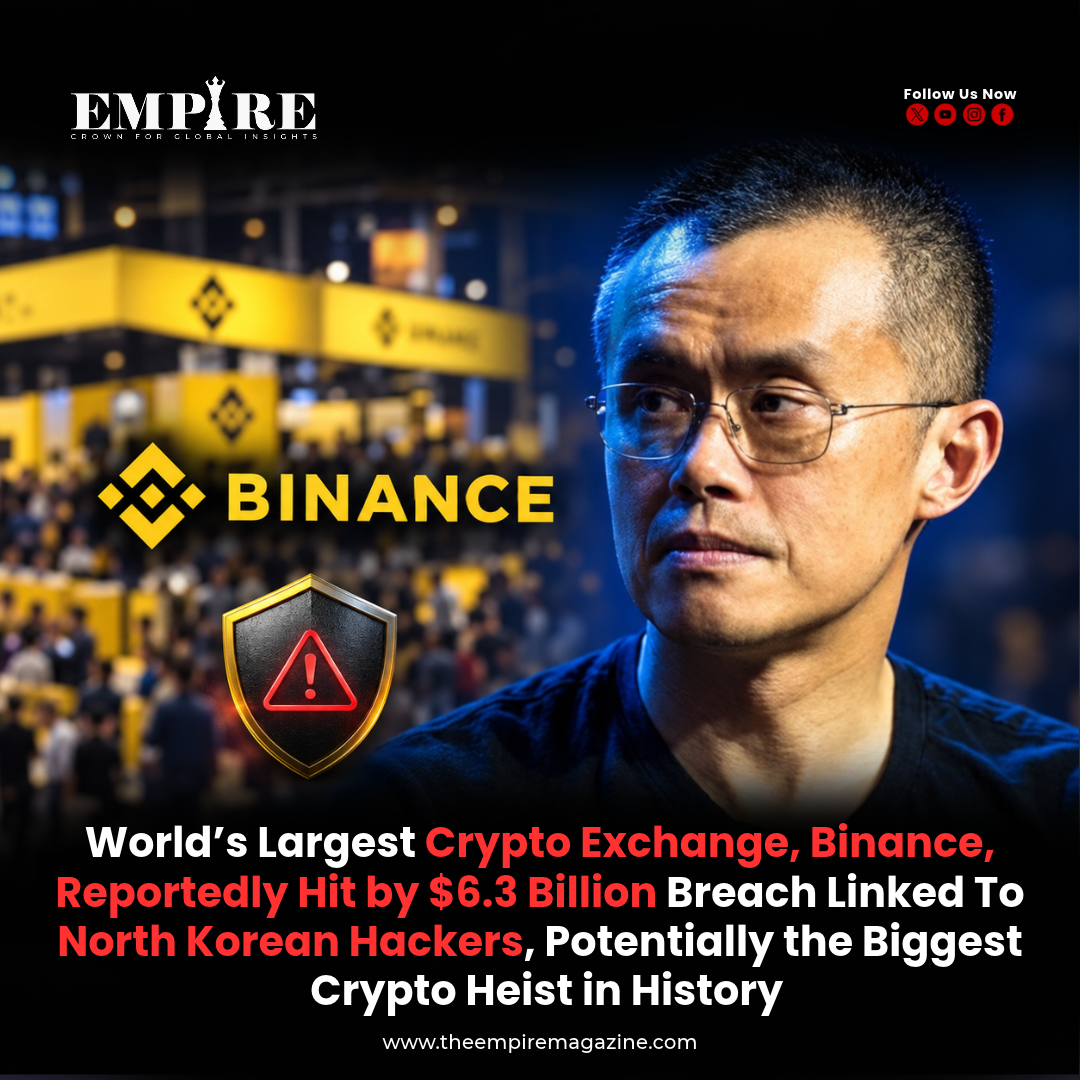
The Binance hack has resulted in approximately US$6.3 billion in stolen cryptocurrency, according to the exchange, after attackers compromised its hot wallets on 29 October 2026.
Blockchain investigators have linked the incident to North Korean hackers. However, responsibility remains under investigation, and the complete sequence of security failures has not yet been established.
Researchers describe the incident as the largest cryptocurrency theft on record. Binance, the world’s largest cryptocurrency exchange, says it will absorb the financial impact while working with law enforcement, blockchain analysts and asset issuers to recover funds.
The immediate challenge extends beyond identifying the attackers. Binance must replace affected assets, restore access to withdrawals and demonstrate that the systems responsible for authorising transactions have been secured.
What Happened in the Binance Hack?
Binance says its hot wallets were compromised at approximately 20:05 UTC on 29 October.
A hot wallet is connected to the internet, allowing an exchange to process transactions quickly. That accessibility makes the security of the surrounding systems and transaction permissions particularly important.
Blockchain intelligence firm TRM Labs reported that attackers moved approximately $6.36 billion across ten blockchains, with most of the transfers occurring within about 20 minutes.
Different investigators have published slightly different estimates:
| Source | Reported amount |
|---|---|
| Binance | Approximately $6.3 billion |
| TRM Labs | Approximately $6.36 billion |
| Elliptic | Approximately $6.43 billion |
These are estimates of the same incident, not separate losses to be added together.
As investigators identify transactions and reconcile affected assets, the final accounting may change. The amount originally stolen also differs from the exchange’s eventual financial loss after recoveries.
How Attackers May Have Accessed Binance’s Systems
Binance’s initial investigation pointed to a potentially compromised laptop belonging to a DevOps engineer. The company said this may have enabled access to an internal service from which unauthorised withdrawal transactions were submitted.
Its subsequent update reported additional points of breach, indicating that the incident involved more than the initial laptop explanation alone.
Binance also said it had found no evidence that wallet private keys were leaked.
That finding does not establish that the withdrawal process remained secure. A system can be compromised through the permissions and services used to approve transactions, even when investigators have not found evidence that the underlying keys were copied.
TRM’s analysis points to a compromise of Binance’s hot-wallet signing infrastructure. The full technical explanation remains subject to the ongoing investigation and the company’s promised incident report.
Why Researchers Suspect North Korean Hackers
TRM Labs attributed the attack to TraderTraitor, a North Korean hacking unit, with high confidence. It said its assessment draws on blockchain evidence and intelligence beyond the public transaction records.
Elliptic also considers North Korean involvement likely. Its investigation identified connections between the movement of Binance’s stolen assets and proceeds from an earlier suspected North Korea-linked attack on Bitget.
Shared Transaction Trails Require Careful Interpretation
Elliptic has also identified limits to that evidence.
A money-laundering network can serve multiple criminals. Finding proceeds from two attacks moving through shared infrastructure does not, by itself, prove that the same people carried out both thefts.
The firm also noted differences from typical North Korea-linked laundering behaviour, including delays in converting stolen stablecoins before issuers froze them.
The evidence supports a suspected connection. A final attribution will require investigators to combine the transaction trails with technical findings and other intelligence.
Approximately $3 Billion Has Been Frozen
Binance says industry partners have helped freeze approximately $3 billion in affected assets.
Stablecoin issuers played a significant role. Tether reported freezing nearly $1.57 billion, while Circle reported freezing more than $800 million linked to the incident.
Those issuer figures form part of the response and should not be added to Binance’s aggregate figure as separate recoveries.
Frozen Funds Have Not Necessarily Been Recovered
Freezing restricts the movement of affected assets. Recovery means those assets have been returned or otherwise restored to the rightful owner.
The distinction matters when assessing how much money remains at risk. An announcement that funds have been located or frozen does not establish that Binance can immediately use them to meet withdrawals.
Elliptic says attackers have also converted some stolen assets into cryptocurrencies that cannot be frozen by a central issuer, making the recovery process more difficult.
How Binance Plans to Cover the Losses
Binance says it will cover losses through its Secure Asset Fund for Users, known as SAFU, and corporate funds.
In its second incident update, the company said it had set aside more than $6.34 billion. Approximately $5 billion was already held in the affected token types, representing roughly 80% of the replacement requirement.
The exchange said it was purchasing the remaining assets through market and over-the-counter transactions.
These figures describe Binance’s stated funding and replacement arrangements. They should be distinguished from money recovered from the attackers.
For customers, the practical outcome depends on both sufficient asset backing and the ability to access funds through functioning withdrawal services.
Latest Status of Binance Deposits and Withdrawals
In its 30 October update, Binance said deposits and unaffected services remained operational, while withdrawals were temporarily suspended.
This clarification matters because some earlier reports described both deposits and withdrawals as paused.
The company plans to restore withdrawals in phases after completing security checks and validating affected systems. Its published restart timetable is a target, subject to those checks.
A promise to cover losses and the restoration of withdrawal access are separate milestones. Customers may retain an account balance while being temporarily unable to transfer assets off the platform.
Why the Theft Is Being Described as a Record
The reported scale substantially exceeds the approximately $1.5 billion stolen from Bybit in February 2025.
The FBI attributed that earlier attack to North Korea and identified the malicious activity as TraderTraitor.
Using Binance’s approximately $6.3 billion estimate, the latest theft is more than four times the size of the Bybit incident.
TRM and Elliptic describe it as the largest known cryptocurrency theft. Comparisons should nevertheless distinguish the value taken at the time of an attack from the final unrecovered amount.
The previous attribution also provides context for investigators. It does not independently establish responsibility for the Binance breach.
What an Updated Proof of Reserves Can Show
Binance plans to publish updated proof-of-reserves results by 2 November 2026, according to its second incident update.
Such a report can provide information about asset holdings and the backing of customer balances at a specified point in time.
Its scope matters. The US Public Company Accounting Oversight Board’s Office of the Investor Advocate has explained that proof-of-reserves reports are not equivalent to financial-statement audits.
Depending on the procedures used, they may not fully address liabilities, ownership obligations or whether assets were borrowed. They also do not establish that an exchange’s internal security controls are effective.
The planned reserve update can therefore help answer questions about asset backing. The technical investigation must separately address how the breach occurred and how the weaknesses have been corrected.
Restoring Access and Confidence
From a business perspective, Binance’s response will be assessed through several concrete outcomes:
- Asset replacement: evidence that affected balances are fully backed.
- Withdrawal restoration: reliable access as services reopen.
- Recovery progress: clear separation of assets traced, frozen and returned.
- Technical accountability: a detailed explanation of the failures and corrective measures.
The Binance hack has placed exchange custody and transaction security under renewed scrutiny. The next stage will depend on verified recovery results, transparent reporting and evidence that customers can safely access their assets again.
Explore more global business, technology and innovation coverage in The Empire Magazine’s article archive.
Read our related coverage: microsoft-voluntary-buyouts-60000-employees/
Follow The Empire Magazine:
Facebook | Instagram
The Empire Magazine | Crown For Global Insights